Guides
Email signatures after a merger or tenant migration
Two companies, two brands and often two Microsoft 365 tenants. How to handle email signatures after a merger, from day one to the tenant move.
Does GDPR apply to email signatures? Yes. A signature is personal data about the person sending it, and a signature service processes more: directory details, and a record of the mail it signs. None of that is a reason not to have one, but your data protection officer will want to know what is shown, what is collected, where it goes and how long it is kept. This post answers those questions in general, and for Footer365 in particular.
A signature shows a person's name, job title, phone numbers and sometimes a photo to everyone they email. Two principles in Article 5 of the UK GDPR are the useful ones here:
A central signature helps with both. You decide once which fields appear, and the details come from your directory rather than from what each person typed years ago.
In Footer365, an empty field is removed from the signature along with its label. So a person who should not show a mobile number simply has none in the directory, and their signature drops the line. The QR code element follows the same principle: the contact card behind it adds details such as job title or phone only when the signature itself shows them.
For the details in your directory, your organisation is the data controller and the signature service is a processor, so you need a data processing agreement with it. Footer365's is published as its data processing terms. The questions to ask any provider:
| Question | Footer365's answer |
|---|---|
| What does it read from the directory? | The user and group attributes needed to build signatures, group membership and your verified domains, through read-only permissions |
| Does it keep copies of email? | No. The relay writes the signature in and hands the message straight back, keeping no copy |
| What does it record about each message? | The sending address, which rule and template applied and how many recipients there were. No recipient addresses and nothing about the content |
| Where is data held? | You choose a data region at sign-up. Footer365's servers are hosted in the United Kingdom |
| Who else is involved? | Listed on the sub-processors page |
Our technical article on data and privacy gives the full list, including how long each kind of record is kept.
Banner campaigns raise the most questions, because tracking a click means recording something about the person who clicked. Footer365 records which campaign and link, when, and whether it looks like an automated link scanner, plus the IP address and user agent of the request for a limited time.
For messages that carried a banner, Footer365 also records which outside organisations the message reached, as email domains only, never addresses. Our guide to click data and privacy covers how to explain this in your own privacy notice.
This is general information rather than legal advice. If your DPO has questions we have not answered here, the security page and data processing terms are the place to start, and the contact page reaches us with anything else.
Start a 30-day trial - no card required.
Two companies, two brands and often two Microsoft 365 tenants. How to handle email signatures after a merger, from day one to the tenant move.
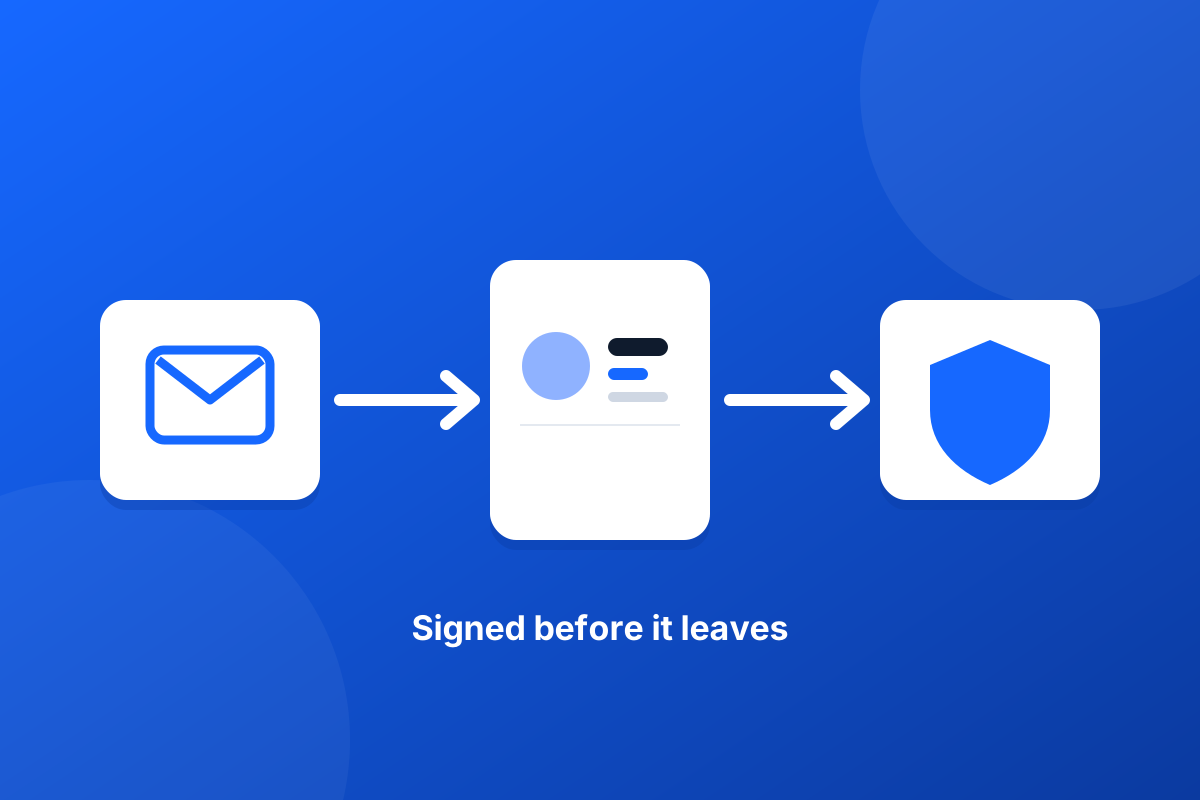
Running Mimecast, Proofpoint or another email gateway? How a server-side email signature fits in the mail flow, what to check, and what never to change.